SSDLC implementation
You've already heard that "Security is not a product, it's a process". That is exactly why we have the Secure Software Development Lifecycle (SSDLC) implementation service.


Many companies’ concept of security equals to ordering penetration tests several times a year. This may and will help in the short term to improve the situation (you will amend the reported bugs), but the next release will repeat the same without any sign of improvement. In the figure below we illustrate the situation in which, as you can see, you are locked in a vicious circle.
It is a much better approach to invest resources in developer training and inviting security consultants at earlier stages of the project. Ideally before the actual designing of the application. The reason can be seen in the graph below:

As you can see, the earlier errors are detected, the less costly it is to fix them. For example, when you invite us to Application Design, we can do Threat modeling and detect any risks before a single line of code is written.
Once a part of the application has been written, it is ideal to do a Source Code Review, which can be done basically at any time and you do not have to wait for the project to finish first.
It is ideal to complement these steps with our developer training, where we will teach them how to program safely, take care of them, and give them a Checklist to use while programming.
This will help you get results soon - developers will produce safer software so you can pay less for penetration tests.

The ideal situation is when we begin the whole cooperation by finding out what your current situation is. To do this, we use OpenSAMM, another OWASP project that allows a thorough assessment of the current situation in the following areas:
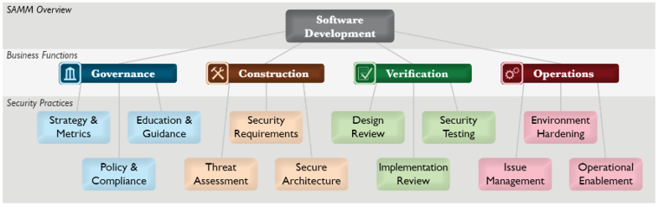
The OpenSAMM analysis output is a list of where you are doing well, and where improvements are needed. It will also help you build a plan that you can follow.

If we have to summarize the SSDLC Implementation Service, this is what it would look like:
- OpenSAMM
- Training and checklist handover delivery
- Threat Modeling
- Source Code Review
- Penetration tests
The SSDLC implementation output is a detailed report evaluating the current state of IT/development, an improvement plan for the given areas, developer support, and technical penetration tests. We can tailor this service for customers so that the outputs are beneficial for small, medium and large businesses.
I'm interested in SSDLC implementation
If you are a web application operator or user, consider reviewing your security and resistance to hacker attacks and other possible threats.
CEO Captes s.r.o., Jan Kopecký
